Palo Alto Networks Cairn at a glance
Palo Alto Networks Unit 42 reported on November 12, 2026 that Chinese-speaking attackers used the open-source Cairn penetration-testing framework, driven by GLM 5.2 and DeepSeek V4, to run 25 autonomous operations against at least 19 organizations, breaching 10.
Ask your AI about this story
Use this story in your business: Unit 42: attackers ran the Cairn AI framework autonomously against 19 organizations (Palo Alto Networks). Ask your AI to explain what happened, how it could affect your business and how to put it to work. It also weighs price, speed, intelligence and the lab behind it. The link to the story is included.
Palo Alto Networks Cairn: status
- Affected
- At least 19 organizations targeted in August–September 2026: seven in the semiconductor and advanced-manufacturing supply chain, three in defense and defense policy, and four in human rights and civil society
- 10 organizations with confirmed unauthorized access or data retrieval, including more than one million member records at a US teachers' union and roughly 150,000 internal documents at an industrial-automation manufacturer
- Systems with authentication bypasses, weak or default credentials, exposed cloud APIs or unpatched known vulnerabilities — the weakness classes the campaign exploited
- CVE identifiers
- Not published
- Last checked
What changed with Palo Alto Networks Cairn
Palo Alto Networks Unit 42 published the investigation on November 12, 2026. From August to September 2026, Chinese-speaking attackers used Cairn, an open-source AI penetration-testing framework, to autonomously conduct 25 operations against at least 19 organizations: seven in the semiconductor and advanced-manufacturing supply chain, three in defense and defense policy, and four in human rights and civil society. The attackers achieved unauthorized access or data retrieval at 10 organizations — including more than one million member records at a US teachers' union, dozens of valid credentials at an industry standards body, and a live standards-ballot document overwritten. Unit 42 tracks the activity as CL-STA-1238 and assesses with moderate confidence that it is China-nexus intelligence collection.
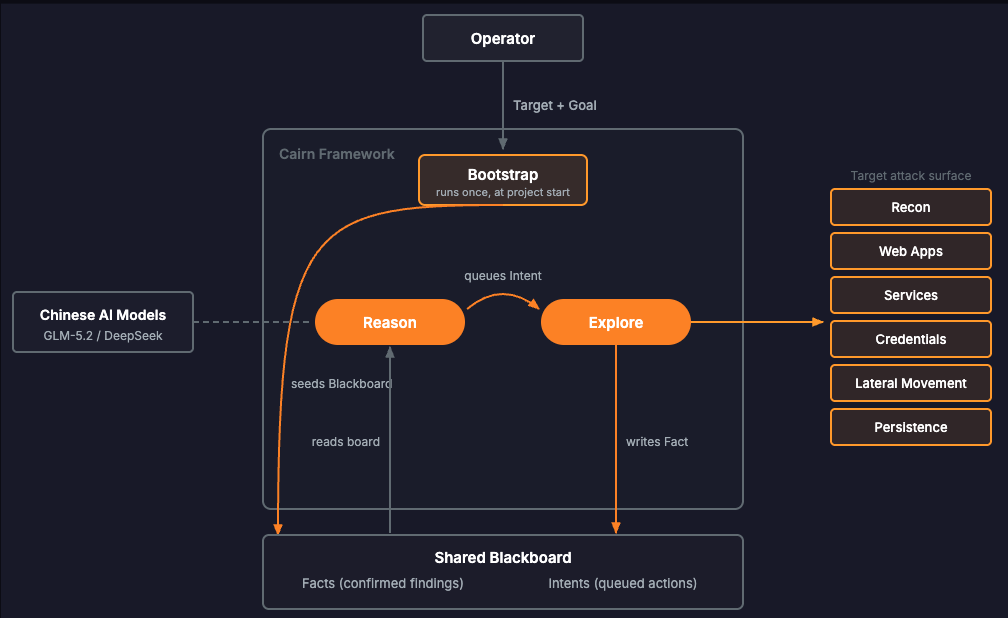
Cairn coordinates AI workers through a shared blackboard of confirmed facts and queued intents: the operator supplies a target and a one-line goal, and the model plans and executes in a Reason–Explore loop until it judges the goal met. The attackers ran 13 operations on Zhipu's GLM 5.2, eight on DeepSeek V4 Flash and four on DeepSeek V4 Pro, from a customized fork hosted in Hong Kong, reinforcing the models with a Chinese-language preamble and an AUTHORIZATION.md file claiming the work was approved; neither model refused. Operations ran from 20 minutes to more than 50 hours against ordinary weaknesses — authentication bypasses, weak and default credentials, exposed cloud APIs and dated public CVEs — and Unit 42 judges the attackers were likely a single operator or small team running simultaneous attempts against all 19 organizations within about two weeks.
How to fix it: Palo Alto Networks Cairn
1. Configuration
Harden identity: remove weak, default and reused credentials, including production passwords shared across accounts — the campaign's most reliable way in was credential weakness, from password spraying to a production credential brute-forced across multiple accounts.
unit42.paloaltonetworks.com (opens in a new tab)2. Configuration
Reduce the exposed attack surface: inventory internet-facing applications, registration endpoints and cloud APIs, because Cairn seeded each operation with a root domain and enumerated the surface on its own.
unit42.paloaltonetworks.com (opens in a new tab)3. Update
Patch known vulnerabilities, including dated public CVEs: Unit 42 found that autonomous AI raised the volume and coverage of exploitation, not its complexity, and that identity hygiene, attack-surface reduction and patching remain effective.
unit42.paloaltonetworks.com (opens in a new tab)
Advisories
Palo Alto Networks Cairn in numbers
Values are copied from the linked source on the date shown. They are not IA Compa measurements.
- Autonomous operations run with Cairnas of · Source for Autonomous operations run with Cairn: unit42.paloaltonetworks.com (opens in a new tab)
- 25
- Organizations targetedas of · Source for Organizations targeted: unit42.paloaltonetworks.com (opens in a new tab)
- 19
- Organizations with confirmed access or data retrievalas of · Source for Organizations with confirmed access or data retrieval: unit42.paloaltonetworks.com (opens in a new tab)
- 10
Why Palo Alto Networks Cairn matters for businesses
Why it matters: the constraint that changed is attacker headcount, not technique. One small team, commodity model APIs and an off-the-shelf framework sustained parallel intrusions that once needed a room of operators — and every breach came through basics a business can fix: weak or reused credentials, exposed APIs, unpatched software. Unit 42's conclusion is that identity hygiene, attack-surface reduction and patching remain effective against autonomous AI attacks, which makes them the highest-value security work a business can fund today — and makes continuous, agent-assisted testing of your own systems a service worth buying before someone runs it against you uninvited.
Get AI News by email
Verified AI stories, each with its official source, on Monday and Thursday mornings. Add breaking news to hear about the biggest ones as soon as we publish them.
Every story links its official source
Free, in English or Spanish
Unsubscribe with one click, any time
Sources for this story
- Attackers Use Autonomous AI to Target Semiconductor, Defense and Civil Society Sectors (opens in a new tab)Official
Palo Alto Networks Unit 42 · unit42.paloaltonetworks.com
Last verified: . IA Compa summarizes public announcements for business readers. We are not affiliated with the companies mentioned. Always confirm details, pricing, and availability with the official source.
- #cairn
- #unit-42
- #autonomous-ai
- #penetration-testing
- #cl-sta-1238
- #glm-5-2
- #deepseek-v4
- #threat-intelligence
- #ai-security
